When Employees Leave, Their Access Should Too
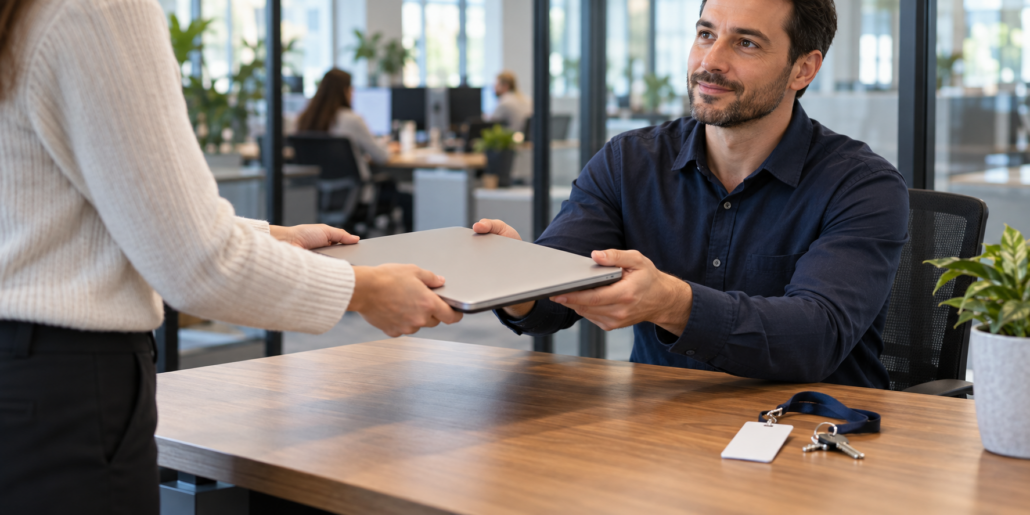
When an employee leaves, there’s usually a familiar checklist: collect the laptop, finish the paperwork, and hand off responsibilities.
But what happens to their access?
Email, shared files, business applications, remote connections, and company social accounts can remain accessible long after someone’s last day. Even an entirely amicable departure can leave gaps if nobody owns the process.
A consistent offboarding plan helps protect company information while keeping the remaining team productive. Here’s what business owners should include and why collecting a computer is only one part of the job.
Start With Clear Ownership and Timing
Offboarding works best when managers, HR, and IT coordinate before the departure.
Someone needs to authorize the changes, confirm the employee’s final working time, and identify who will take over their responsibilities. IT then needs enough information to prepare the appropriate access changes.
For a planned departure, some handoffs can happen beforehand. Other situations require access to be restricted at a specifically coordinated time.
Avoid vague requests like “remove access sometime Friday.” A clear schedule and named responsibilities reduce confusion, especially when multiple systems and outside providers are involved.
Keep departure details limited to the people who need them.
Look Beyond the Email Account
Disabling email is important, but it doesn’t cover every place an employee might have access.
Think about your accounting software, customer relationship management platform, file-sharing tools, vendor portals, website, password manager, and remote access services. Some may use a central company login; others may have separate credentials.
Maintain an application inventory and use it during offboarding. Ask the employee’s manager about department-specific tools that IT may not manage directly.
Include privileged accounts and account recovery settings in the review.
A complete access list makes it easier to remove permissions without overlooking the smaller applications that still hold valuable information.
Address Existing Sessions
Changing a password should not be treated as proof that all access has ended.
Depending on the system, an employee may still have an active session on a phone, browser, or other device. Your IT team should evaluate how to block future sign-ins and revoke existing sessions appropriately.
Some applications manage their own sessions and require separate action. Microsoft’s guidance specifically notes that its identity platform cannot directly revoke every session issued by another application.
This is why offboarding should follow documented steps for your environment rather than rely on a single password reset.
The goal is verified access removal across the relevant systems.
Preserve Information Before Deleting Accounts
Removing access and deleting information are different tasks.
Before accounts or licenses are removed, determine what business records need to remain available and who is authorized to access them. That may include project files, customer correspondence, shared documents, and work stored in an individual cloud account.
Follow your retention requirements and any applicable legal holds. Your IT team should also confirm platform-specific consequences before making changes that could affect data availability.
Microsoft’s offboarding guidance includes both restricting former employees’ access and preserving appropriate access to their email and files.
Plan the sequence so security changes don’t accidentally interrupt business continuity.
Transfer Responsibilities Securely
Your team may need to monitor incoming requests, continue a project, or manage a system the departing employee previously owned.
Arrange approved access for the appropriate replacement. Avoid sharing the former employee’s password or allowing others to continue working under their identity.
Review ownership of shared calendars, recurring reports, automated workflows, and important vendor relationships. Update recovery contacts where a departing employee’s phone number or email address is attached.
If shared credentials were used, identify which need to be changed and who depends on them.
A thoughtful handoff helps your team keep working without preserving unnecessary access for the person who left.
Account for Devices and Physical Access
Collect company-owned laptops, phones, removable drives, keys, badges, and security tokens. Compare what comes back with your equipment records.
For remote employees, arrange a return process with clear instructions and tracking.
Company information on personal devices needs separate consideration. Any removal should follow your organization’s policies, employee agreements, and device-management capabilities. A targeted removal of company data is different from wiping an entire personal device.
Physical access matters, too. Coordinate changes to building credentials and other access systems.
Document outstanding items and assign someone to follow up rather than assuming everything has been returned.
Finish With Verification
A checklist is useful only when someone confirms the work.
Record which accounts were restricted, how information was preserved, what ownership changed, and whether equipment remains outstanding. Resolve exceptions.
At Remington Computer Service, we help businesses make technology transitions more manageable. A clear employee offboarding process protects access, supports continuity, and gives your team fewer loose ends.
If your current process stops at collecting the laptop, let’s talk about completing the picture.
Remington Computer Services has been serving the Rhode Island, Connecticut and Massachusetts area since 2010, providing IT Support such as technical helpdesk support, computer support and consulting to small and medium-sized businesses. Our experience has allowed us to build and develop the infrastructure needed to keep our prices affordable and our clients up and running. Schedule a complimentary consultation today.



Leave a Reply
Want to join the discussion?Feel free to contribute!